About 22 Security
Setting the standard for penetration testing and security advisory
Founding ideas
Penetration testing should start where attackers do.
Too often a narrowly scoped application test on a sub-prod environment gives companies a false sense of security. Today’s malicious actors are using AI to discover weaknesses throughout your estate with the goal of making initial entry and then pivoting to the sensitive data. Using AI to run the same limited scope penetration test is not enough.
22 Security starts with an estate-wide view of a company’s digital footprint. Every penetration test includes at least a passive assessment of the estate and reports whatever vulnerabilities, misconfigurations, and indicators we can deduce.
Security and compliance should accelerate the business,
not drag on it.
A SOC 2 report, ISO 27001 or HITRUST certification, HIPAA assessment, or GDPR compliance program unlocks markets and revenue. Your deal pipeline depends on getting through each customer’s third-party assessment quickly. That takes controls that are effective and efficient to operate, mapped correctly to both the standards frameworks and your customers’ requirements. It also means presenting the program the way the customers and auditors reviewing it expect to see it. 22 Security builds programs that accelerate the business.
When everything is a priority, nothing is.
Scanners hand engineering teams long lists sorted by vendor severity. We keep the vendor’s severity on every finding and set our own priority next to it. Priority depends on your environment: which systems and data stores are your critical assets and whether a finding sits on an attack path to one of them. Engineering time goes to the fixes that matter first.
Trusted by security teams all over the world
- companies checked
- 40,000+
- subdomains mapped
- 925,000+
- findings on record
- 330,000+
- companies fixed what we reported
- 90+
Team
Meet the team
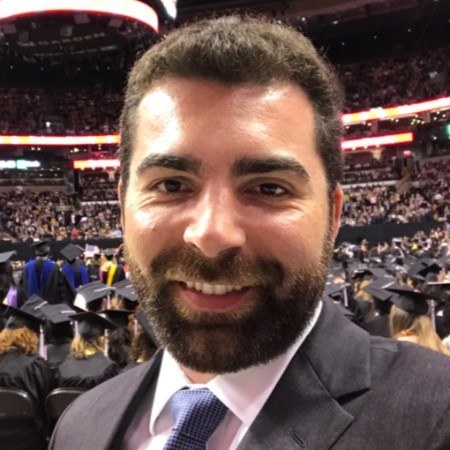
Founder’s background
John built the technology programs inside two successful startups full time, then evaluated the cybersecurity of 171 more companies running third-party risk assessments at a Fortune 200 global bank.
John is a cybersecurity subject matter expert and a business leader. He earned an MBA and a second master’s degree in finance. He then went on to earn the CISSP, CISM, CISA, CCSP and 7 AWS certifications.
John currently lives in North Carolina with his wife Micayla, who is the 22 Security Business Operations Manager.
Start with a conversation.
The right engagement depends on what you’re building and where the gaps are. A 30-minute call gets us to whether and how we can help.